Category: blog
Backup
Cloud platforms provide availability.
They do not replace an independent backup strategy.
Deleted files, compromised accounts, ransomware, misconfigured retention, and service outages can still affect business data.
A cloud-era backup plan requires:
- Multiple copies
- Separate storage locations
- Immutable recovery points
- Access controls
- Continuous monitoring
- Tested restores
The 3-2-1 backup rule remains a practical baseline for small businesses.
The 3-2-1 Rule
The rule requires:
- 3 copies of business data
- 2 different storage media or systems
- 1 copy stored offsite
The production system counts as one copy.
Two additional backup copies are required.
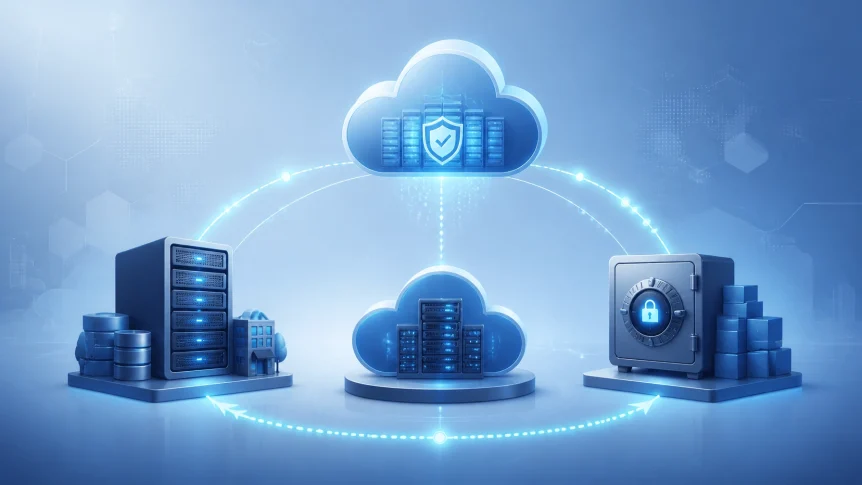
A small business implementation could include:
- Original data on a server, workstation, or cloud application
- Local backup on a backup appliance or NAS
- Offsite cloud backup in a separate facility
Local backups support faster file and system recovery.
Cloud backups provide geographic separation.
Both are required for broader coverage.

3-2-1-1-0 for Ransomware Resilience
The standard rule can be extended to 3-2-1-1-0.
Additional controls:
- 1 immutable or air-gapped copy
- 0 unverified backup errors
An immutable backup cannot be modified or deleted during its retention period.
An air-gapped backup is separated from production systems and credentials.
The additional protection matters because ransomware can target:
- Production servers
- Workstations
- Network shares
- Backup repositories
- Cloud administration accounts
- Synchronization platforms
A connected backup is not automatically a protected backup.
If compromised credentials can delete every recovery point, the backup design has a single point of failure.
Immutability
Immutability uses write-once, read-many storage behavior.
Data is written to the backup repository.
Retention policies prevent changes until the defined expiration date.
Common implementation methods include:
- Object Lock
- WORM storage
- Immutable backup repositories
- Locked cloud vaults
- Separate cloud accounts
- Separate tenants or subscriptions
- Dedicated backup credentials
The immutable copy should not share administrative access with production systems.
Recommended controls:
- Retention lock enabled
- Separate administrator accounts
- MFA required for backup administration
- RBAC applied to backup policies
- Encryption enabled in transit and at rest
- Encryption keys managed separately
- Backup deletion restricted
- Audit logging retained

Immutability does not replace malware detection.
It preserves recovery points.
Restore procedures are still required to identify a clean recovery point and return systems to operation.
Identify Critical Data
Backup policies should be based on business impact.
Inventory all data and systems:
- File servers
- Microsoft 365 data
- Google Workspace data
- Databases
- Accounting platforms
- CRM systems
- Line-of-business applications
- Virtual machines
- Network configurations
- Endpoints
- Website files
- Email archives
- Cloud storage
- Domain and DNS records
Cloud synchronization is not the same as backup.
Synchronization can replicate:
- Accidental deletions
- Malicious changes
- Corrupted files
- Encrypted ransomware files
Independent backup copies are required.
Classify systems by recovery priority.
Critical systems require shorter recovery windows and more frequent backup jobs.
Less critical data may use longer intervals and retention periods.
Define RPO and RTO
Two values guide backup design.
Recovery Point Objective
RPO defines the maximum acceptable data loss.
Examples:
- 24-hour RPO
- 4-hour RPO
- 1-hour RPO
- Near-continuous replication
A business processing transactions throughout the day may require more frequent protection than a business working primarily with static documents.
Recovery Time Objective
RTO defines how quickly a system must be restored.
Examples:
- Restore individual files within minutes
- Restore a server within several hours
- Restore core operations within one business day
RPO and RTO determine:
- Backup frequency
- Local storage requirements
- Cloud bandwidth needs
- Retention periods
- Recovery infrastructure
- Service costs
They should be documented for each critical workload.
Set Backup Frequency and Retention
A baseline schedule may include:
- Daily incremental backups
- Weekly full backups
- Monthly recovery points
- Longer retention for legal or tax records
Some workloads require more frequent protection.
Examples:
- Financial databases
- Customer records
- Active project files
- Transaction systems
- Shared production documents
Retention should account for delayed detection.
Ransomware may remain unnoticed for days or weeks.
A backup retained for only a few days may contain no clean recovery point.
Retention requirements may also be affected by:
- Industry regulations
- Customer contracts
- Tax rules
- Legal holds
- Internal records policies
- Cyber insurance requirements
Document the reason for each retention period.
Secure the Backup Environment
Backups contain business data.
They require the same security controls applied to production systems.
Minimum controls:
- Encryption at rest
- Encryption in transit
- MFA for administrative access
- Separate backup administrator accounts
- Least-privilege permissions
- Network segmentation
- Restricted repository access
- Endpoint security on backup servers
- Patch management
- Centralized logging
- Alerting for deletion attempts
Backup credentials should not be reused across production systems.
Service accounts should have only the permissions required to complete backup operations.
Administrative access should be reviewed periodically.
Unused accounts should be removed.
Backup storage should not be exposed directly to the public internet unless the architecture requires it and additional controls are applied.
Monitor Every Backup Job
A completed schedule does not prove usable protection.
Monitoring should verify:
- Job completion
- Data coverage
- Repository capacity
- Failed files
- Backup age
- Replication status
- Encryption status
- Malware scanning results
- Immutable retention status
- Cloud connection status
Alerts should be generated when:
- A backup fails
- A system stops reporting
- Storage capacity reaches a threshold
- A new server is not protected
- Retention settings change
- Backup data is deleted
- Replication stops
- Restore validation fails
New systems must be added to backup policies during deployment.
Unprotected assets are common after:
- Server replacements
- Cloud migrations
- Employee onboarding
- Application changes
- Network redesigns
- Mergers or acquisitions
The X-Tek managed IT services approach includes continuous monitoring and proactive maintenance. Backup status can be reviewed as part of broader infrastructure management.
Test Restores
An untested backup is an assumption.
Restore testing should include:
- Individual files
- Folders
- Mailboxes
- Databases
- Virtual machines
- Complete server images
- Application dependencies
- Configuration files
Suggested schedule:
- Monthly file-level restore test
- Quarterly system-level restore test
- Annual disaster recovery exercise
- Additional testing after major infrastructure changes
Record:
- Date and time
- System tested
- Recovery point used
- Restore duration
- Data validation result
- Problems identified
- Corrective actions
- Assigned owner
Testing should verify that recovered data can be opened and used.
A successful job status is not enough.
The recovery process must also be documented.
At least two people should know how to initiate recovery.
Vendor contact details, credentials, recovery keys, and escalation procedures should be stored securely and made available during an incident.

Include Cloud Applications
Cloud applications require separate consideration.
Microsoft 365 and Google Workspace provide availability and platform redundancy.
They may not provide the retention, recovery granularity, or independent protection required by your business.
Review backup coverage for:
- Shared drives
- OneDrive or SharePoint data
- Google Drive files
- Calendars
- Contacts
- Collaboration content
- User accounts
- Deleted items
- Retention policies
Cloud migration planning should include backup architecture from the beginning. X-Tek’s cloud migration guidance for small and medium-sized businesses identifies backup solutions as an early migration consideration.
X-Tek Managed Backup Services
X-Tek can manage backup operations for small businesses that do not maintain dedicated backup administration internally.
Managed backup services may include:
- Backup environment assessment
- Data and system inventory
- 3-2-1 architecture planning
- Local and cloud backup configuration
- Immutable storage configuration
- Backup monitoring
- Failure alerts
- Retention management
- Restore testing
- Recovery documentation
- Disaster recovery planning
- Ongoing policy review
Coverage can be aligned with existing server, PC/Mac, cloud, network, and security requirements.
X-Tek provides business IT support, cloud services, infrastructure management, and related solutions.
The operating model:
- Systems are monitored
- Backup jobs are verified
- Failures are reported
- Recovery points are tested
- Issues are remediated
- Policies are updated as infrastructure changes
Small Business Backup Checklist
Use this checklist during a backup review.
- Three total copies exist
- Two storage systems or media types are used
- One copy is stored offsite
- One copy is immutable or air-gapped
- Backup credentials are separate from production credentials
- MFA protects administrative access
- Encryption is enabled
- Critical systems have defined RPOs
- Critical systems have defined RTOs
- Backup failures generate alerts
- New systems are added to backup policies
- Cloud applications are included
- Monthly restore tests are completed
- Quarterly system restores are completed
- Recovery procedures are documented
- At least two people can execute recovery
- Retention meets business and compliance requirements
Contact Information
Business Solutions Information Request:
https://xtekit.com/business-solutions-information-request/
815-516-8075