Category: blog
Network security monitoring is not about collecting every available log.
It is about identifying events that indicate:
- Account takeover
- Privilege abuse
- Lateral movement
- Data theft
- Ransomware preparation
- Security-control failure
- Unauthorized configuration changes
For SMBs, monitoring should focus on a defined set of high-value events.
X-Tek provides network monitoring, infrastructure maintenance, security monitoring, and managed IT support for businesses that need continuous visibility without building an internal security operations team.
Review X-Tek business IT and infrastructure services
1. Login and Authentication Activity
Authentication events provide the starting point for most investigations.
Monitor logins across:
- Microsoft 365 or Google Workspace
- Active Directory
- VPN systems
- Firewalls
- Servers
- Remote Desktop
- Cloud applications
- Administrator consoles
- Endpoint management tools
Important events include:
- Repeated failed logins
- Account lockouts
- Successful login after multiple failures
- Login from a new country or IP address
- Login from an unfamiliar device
- Login outside normal working hours
- Impossible travel between locations
- First-time VPN or remote-access use
- Dormant account activity
- Terminated employee account activity
- Administrator login from a standard workstation
- Service-account use outside its normal function
- MFA failure or MFA removal
Each event should record:
- Username
- Timestamp
- Source IP
- Device
- Authentication method
- MFA result
- Target system
- Success or failure
A single failed login is usually not an incident.
A successful login from an unusual location followed by access to sensitive systems requires investigation.
X-Tek monitoring can be configured to identify authentication patterns that differ from normal business activity.
2. Privilege and Account Changes
Attackers often seek administrative access after entering a network.
Privilege changes should be treated as security events, not routine administrative noise.
Monitor:
- New user accounts
- Deleted accounts
- Re-enabled accounts
- Password resets
- MFA changes
- Group membership changes
- New administrator roles
- Delegated permissions
- Service-account changes
- File-share permission changes
- Cloud application role changes
- Backup administrator changes
High-priority alerts include:
- A standard user becoming an administrator
- MFA being disabled
- A privileged account being created outside the change process
- A user receiving access to a critical server
- A backup operator role being assigned unexpectedly
- A terminated employee account being reactivated
- A service account being used interactively
Privilege events should be matched against approved change records.
If there is no ticket, request, or documented approval, the change requires review.
The CISA logging guidance for small and medium-sized businesses recommends recording user activity, administrator actions, application logins, and system events.
3. Remote Access and Lateral Movement
Remote access is required for many businesses.
It also provides a direct path into internal systems.
Monitor:
- VPN connections
- Remote Desktop sessions
- SSH access
- Remote management tools
- Administrative shares
- Directory-service activity
- Server-to-server connections
- Workstation access to file servers
- Cloud management sessions
Look for:
- A workstation user connecting to a server for the first time
- One account accessing multiple systems in a short period
- Remote access from an unfamiliar device
- RDP activity outside approved hours
- A new remote-management application
- A user accessing systems unrelated to their role
- Rapid access to many file shares
- Administrative tools launched from a standard endpoint
- Unusual PowerShell or scripting activity
The key question:
Who connected, from where, to what, and what happened next?
Identity records alone are not enough.
Firewall records, endpoint data, VPN logs, and server logs should be correlated when possible.
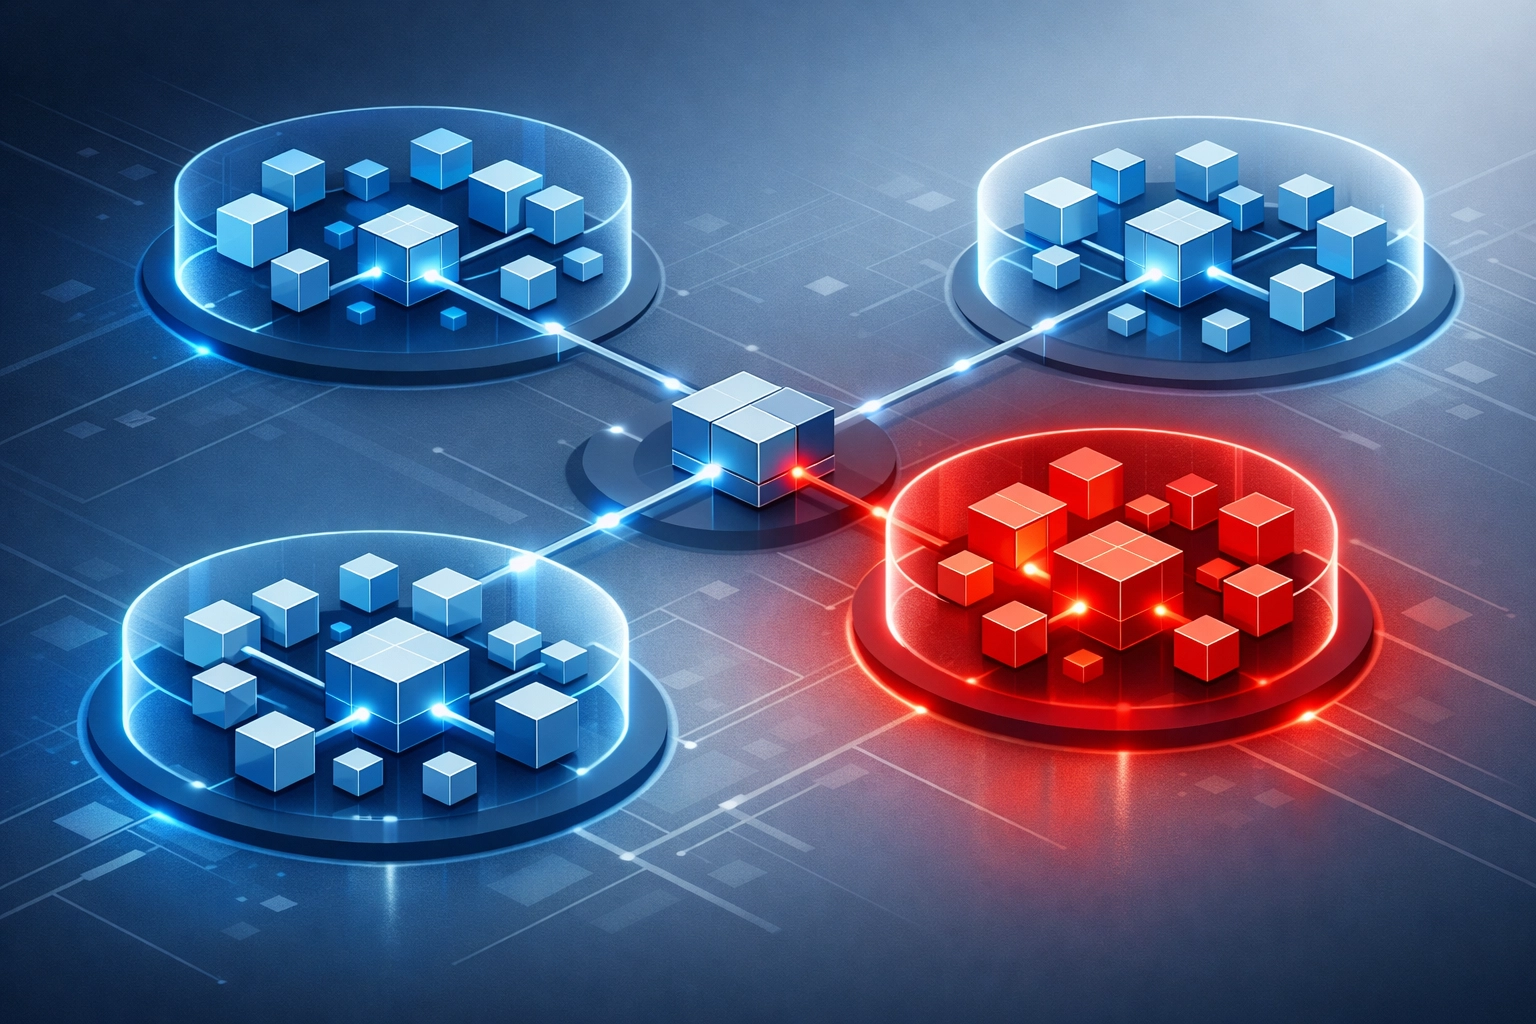
Network segmentation limits the number of systems that can be reached after one account or device is compromised.
X-Tek supports network design, equipment maintenance, firewall configuration, and infrastructure monitoring as part of its business technology services.
4. Data Access and Transfers
Data movement can indicate theft, ransomware, unauthorized disclosure, or a compromised account.
Monitor access to:
- Financial records
- Customer databases
- Human resources files
- Legal documents
- Intellectual property
- Shared drives
- Cloud storage
- Email systems
- Business applications
- Backup repositories
Relevant events include:
- Mass file reads
- Mass file changes
- Bulk downloads
- Large outbound transfers
- Uploads to unfamiliar cloud services
- Transfers to consumer file-sharing platforms
- New external destinations
- Unusual DNS requests
- Unusual encrypted outbound traffic
- Data transfers outside normal business hours
- Access to files unrelated to the user’s role
There is no universal data-transfer threshold that fits every business.
A law firm, manufacturer, and medical office will have different normal activity.
Monitoring should establish a baseline, then identify material deviations.
Record:
- User
- Source device
- Destination
- Protocol
- Data volume
- File count
- Time
- Application
- Accessed location
File content may not be visible because of encryption or privacy controls.
Metadata still provides useful evidence.
A large transfer from a finance workstation to an unfamiliar external service should be reviewed even when the file contents cannot be inspected.
5. Firewall and Network Configuration Changes
Firewall changes can create exposure without producing an obvious malware alert.
Monitor changes to:
- Firewall rules
- NAT settings
- Port forwarding
- VPN configuration
- DNS
- Routing
- Wireless security
- IDS and IPS settings
- Allow lists
- Deny lists
- Logging policies
- Traffic inspection
- Network segmentation
High-risk changes include:
- Opening an inbound management port
- Allowing traffic from the entire internet
- Disabling inspection
- Removing a deny rule
- Changing VPN authentication
- Adding an unfamiliar external IP address
- Permitting broad access between network segments
- Reducing log retention
- Disabling firewall notifications
Every change should include:
- Person making the change
- Previous value
- New value
- Timestamp
- Source system
- Approval or ticket
- Reason
- Rollback status
A firewall modification outside an approved maintenance window should generate an alert.
The Microsoft firewall auditing documentation provides examples of firewall and IPsec events that can support this monitoring.
6. Backup and Recovery Activity
Backup systems are direct targets during ransomware incidents.
Monitoring should cover backup operations, backup administration, and recovery testing.
Watch for:
- Failed backup jobs
- Missed backup jobs
- Unusual backup volume
- Backup-agent shutdown
- Backup credential changes
- Retention-policy changes
- Snapshot deletion
- Repository deletion
- Backup-console logins
- Unexpected restore requests
- Restore failures
- Unusual encryption activity
- Backup traffic from an unfamiliar host
- Mass changes to backup sets
A backup that has not been tested is an assumption.
A successful job does not prove that files can be restored.
Review:
- Backup completion
- Backup integrity
- Recovery point age
- Recovery time
- Restore-test results
- Offline or isolated copy availability
- Administrative access
- Retention settings
The CISA ransomware guide recommends offline or otherwise protected backups, encryption, MFA for backup administration, and regular restoration testing.
X-Tek includes security and backup monitoring as part of its managed IT approach.
Backup failures should not remain in a ticket queue for several days.
They should be reviewed based on business impact and recovery requirements.
7. Security-Control Failures
A missing security signal can be as important as a security alert.
Monitor when:
- Antivirus is disabled
- EDR stops reporting
- Logging is disabled
- Audit settings are changed
- Firewall protection stops
- Time synchronization fails
- Tamper protection is disabled
- Agents stop communicating
- Logs are cleared
- Log retention is reduced
- Monitoring credentials expire
A silent endpoint should produce an alert.
A cleared security log should produce an alert.
A system that has stopped reporting should not be treated as healthy.
Centralized logs should be protected from unauthorized changes and deletion.
NIST log-management guidance covers the generation, transmission, storage, access, and disposal of log records used for security operations and investigations.
What X-Tek Network Security Monitoring Should Produce
Monitoring is useful only when alerts lead to assigned actions.
A practical SMB monitoring process should include:
Immediate alerts
- Suspicious successful login
- New administrator account
- MFA disablement
- Unexpected firewall exposure
- Backup deletion
- Security-control shutdown
- Ransomware-like file activity
- Large anomalous outbound transfer
Daily review
- Privileged login activity
- Failed administrator logins
- Remote-access events
- Backup failures
- Firewall changes
- Unusual outbound connections
- Endpoints not reporting
Weekly review
- New accounts
- Admin-group membership
- Inactive accounts
- Top outbound destinations
- Configuration exceptions
- Repeated alert patterns
- Sensor coverage
Monthly review
- Restore testing
- Log-retention review
- Access review
- Firewall-rule review
- Baseline tuning
- Incident-response exercises
- Removal of stale accounts and rules
Every alert should identify:
- Severity
- Responsible reviewer
- Expected response
- Escalation contact
- Required documentation
- Closure criteria
The goal is not thousands of notifications.
The goal is reliable detection of unusual identity, privilege, network, data, firewall, backup, and security-control activity.
X-Tek can assess current monitoring coverage, identify gaps, and support ongoing network security operations.
Request business solutions information
Sources
- CISA Use Logging on Business Systems
- CISA StopRansomware Guide
- NIST Cybersecurity Log Management Planning Guide
- Microsoft Firewall Auditing and Logging
- CISA Logging Made Easy
Contact Information
Business Solutions Information Request:
https://xtekit.com/business-solutions-information-request/
815-516-8075